
Falconfeeds.io is the latest addition to ThreatStream's leading repository of global threat intelligence sources, and includes a massive database of real-time threat intelligence from over 10M+ global sources across dark web, deep web, and open channels.
Falconfeeds.io is an automated threat intelligence service that vigilantly monitors and delivers the latest security incidents and insights on threat actors from around the globe, around the clock. Their expansive coverage includes threat data from the surface web, deep web, dark web, Tor networks, Telegram channels, and other hidden sources, and surfaces real-time alerts through proactive threat intelligence gathering.
Activating Falconfeeds Intelligence in ThreatStream
As a premium feed, activating Falconfeed's intelligence requires a subscription to Falconfeed's Unified Threat Intelligence Pipeline. Setting up the feed in ThreatStream is quick and easy – users simply activate the Falconfeeds tile within the ThreatStream APP store and provide their Token from Falconfeeds.
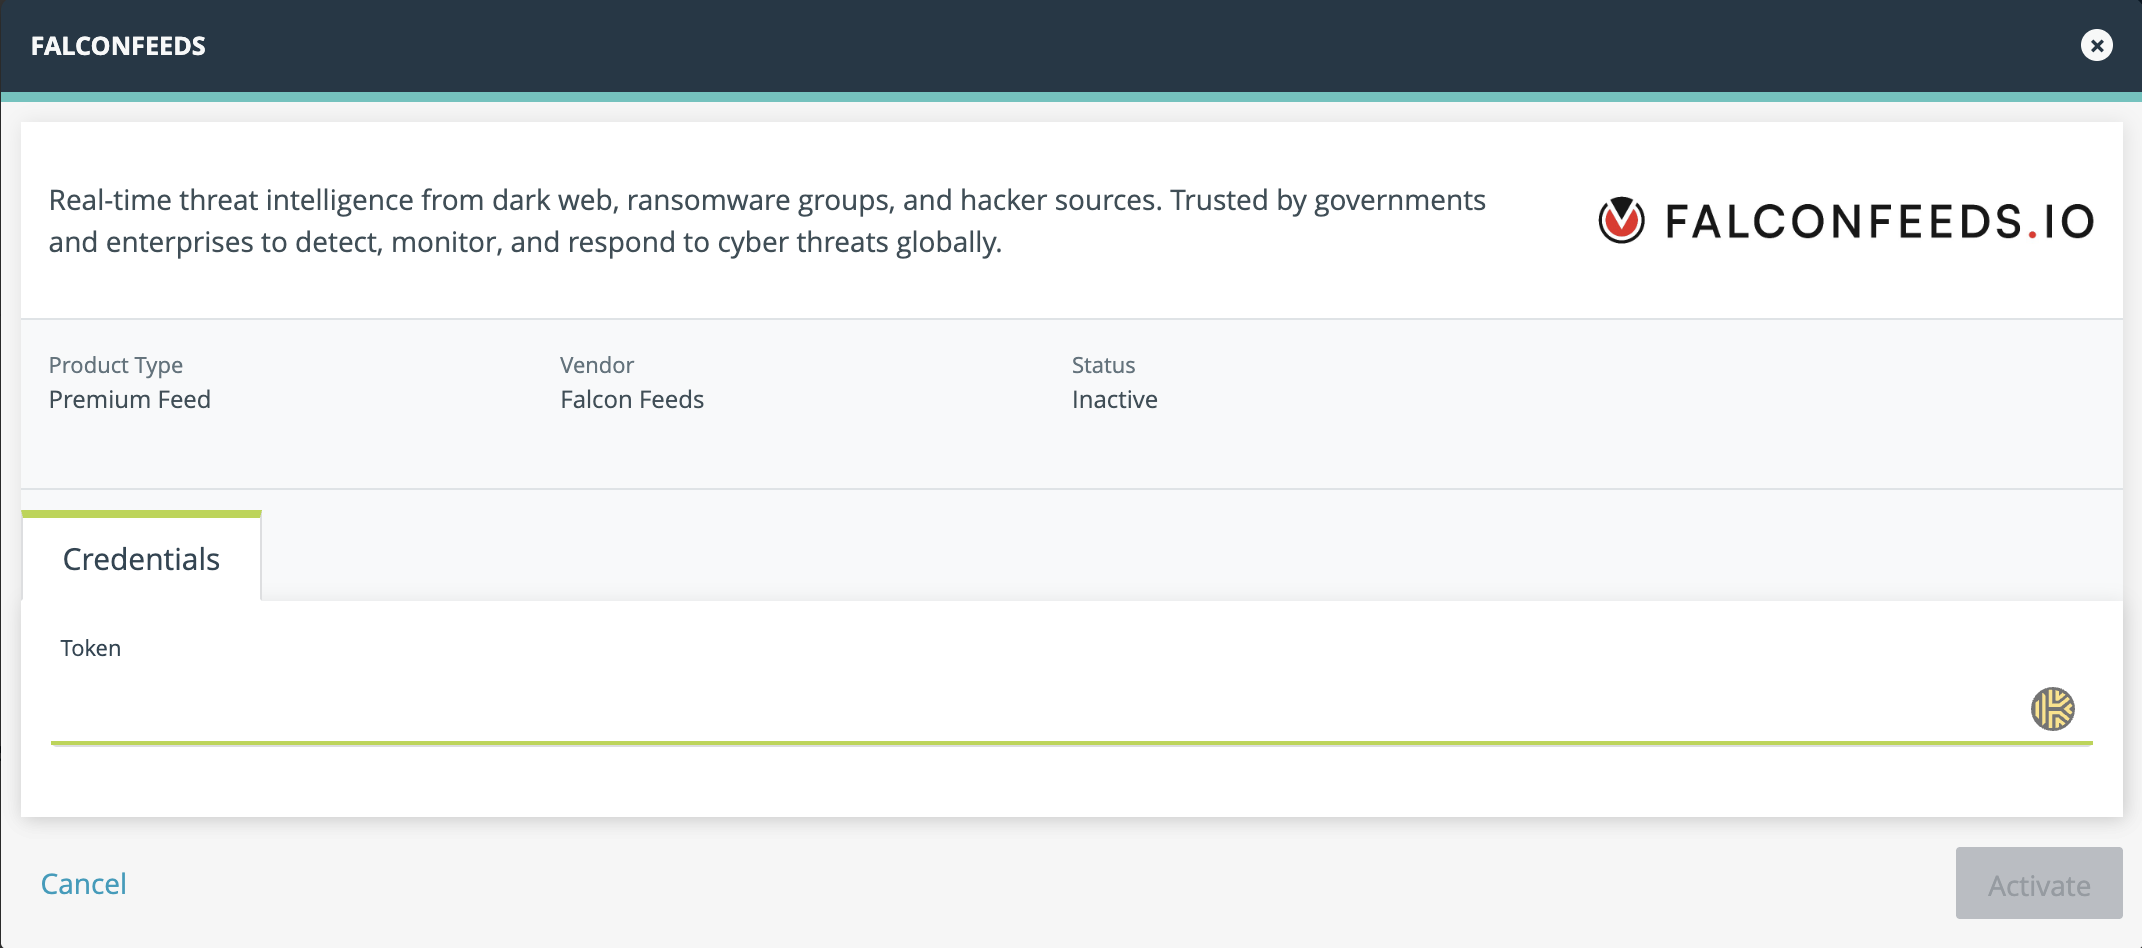
Get Started with Falconfeeds and ThreatStream
Visit the Falconfeeds website to learn more about its threat intelligence offerings, or schedule a demo with Anomali to see how ThreatStream provides access to the industry's largest curated global repository of threat intelligence, including new premium intel from Falconfeeds.
FEATURED RESOURCES
Crypto Exchange Security: The Financial Cost of Chronic Failures and the Regulatory Reckoning Ahead