
The Anomali team is excited to now offer Mandiant Digital Threat Monitoring within the ThreatStream APP store. Digital Threat Monitoring is a threat intelligence feed offered by Mandiant, now part of Google, that monitors open, deep, and dark web sources to detect data leaks, brand abuse, credential exposure, and ransomware threats in near real-time using Mandiant’s threat intelligence and machine learning.
Monitor the Open, Deep, and Dark Web
The Mandiant Digital Threat Monitoring feed offers great visibility into the following threats:
- Compromised credential exposure — both for internal employee and customer data
- Malicious targeting or potential attacks based on deep and dark web activity
- Malicious or accidental insider data leaks
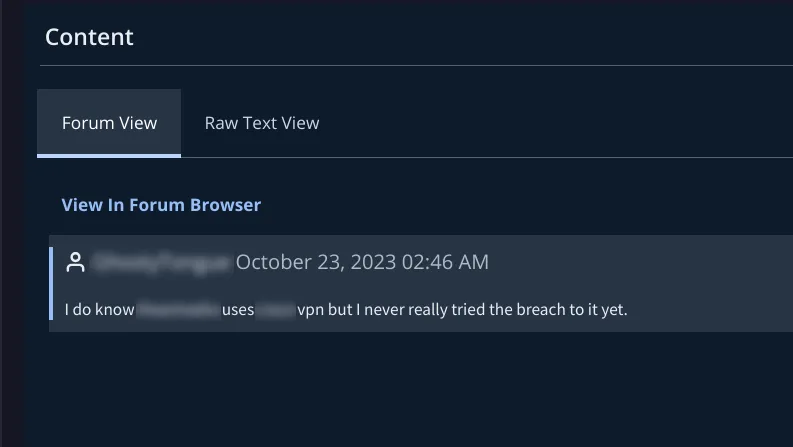
The feed closely monitors locations on the web where credentials or data breaches are traded or sold, such as dark web markets, blogs, forums, paste sites, and more. You can learn more about Mandiant Digital Threat Monitoring in this datasheet.
Enabling Mandiant Digital Threat Monitoring in ThreatStream
By enabling Mandiant Digital Threat Monitoring in Anomali ThreatStream, CTI teams can correlate Mandiant's threat intelligence with other intel sources and distribute this intelligence throughout their organization's security telemetry. Anomali ThreatStream helps to automatically contextualize, deduplicate, and define the severity/confidence of potential threats. ThreatStream users can also share and distribute this intelligence among Trusted Circles.
As a premium feed, accessing this data requires an active subscription with Google for Mandiant Digital Threat Monitoring. To enable the feed in ThreatStream, users can simply:
- Access the "Mandiant DTM" tile within the ThreatStream APP Store
- Submit the "Client_key" and "Client_ secret" values provided by Mandiant DTM
- Click "Activate" and the feed should now be active
Get Started in ThreatStream
Interested in exploring the integration between Mandiant Digital Threat Monitoring and Anomali ThreatStream? If you're not yet a ThreatStream customer, request a demo to see the integration for yourself along with the 200+ other threat intelligence feeds available in the ThreatStream APP Store.
FEATURED RESOURCES
Shadow AI in the Enterprise: Why Unapproved AI Tool Adoption Is Becoming a Systemic Data Governance Crisis